Experts Urge Stronger Human Oversight and Accountability as AI Raises Cybersecurity Risks Across Africa
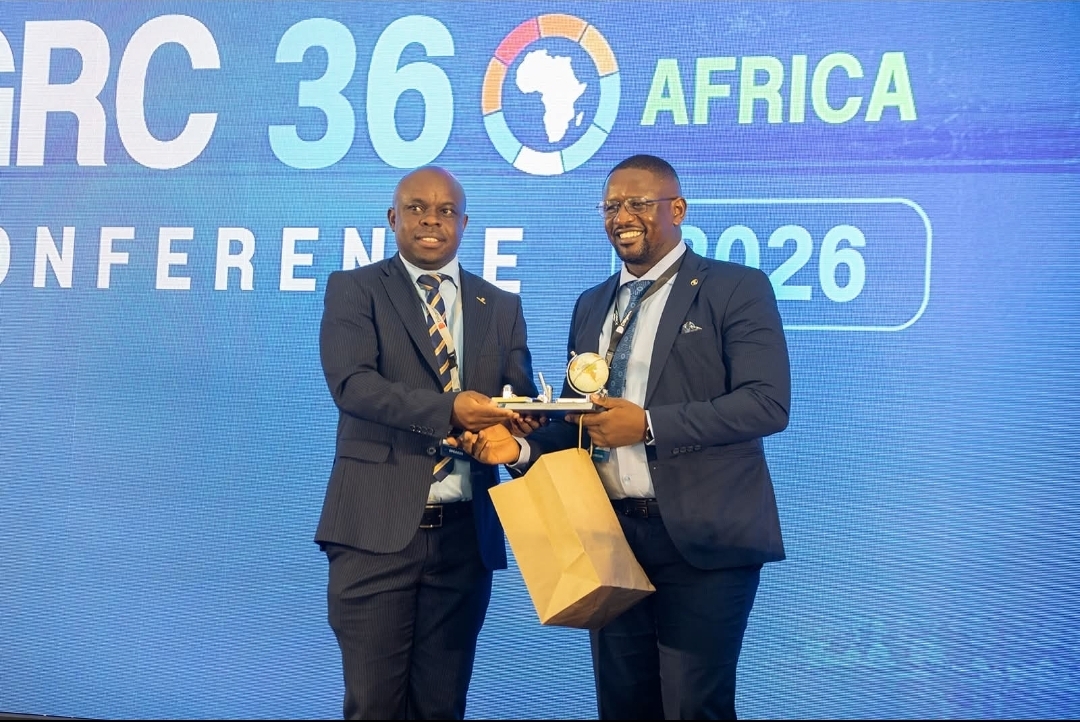
Experts at the ISACA Kenya Chapter’s GRC 360° Africa Conference 2026 in Naivasha have called for stronger human oversight, accountability and governance in artificial intelligence adoption. Internal Auditor-General at the National Treasury, Dr Sammy Kimunguyi, warned that AI is making cyberattacks more sophisticated through voice imitation and convincing fake videos. He emphasised the need to protect critical information infrastructure, strengthen incident response and comply with data protection and cybercrime laws. ISACA Kenya Chapter President Bonface Asiligwa cautioned that rapid AI adoption without adequate governance frameworks, organisational preparedness and regulation could expose institutions to significant risks. The conference brought together governance, cybersecurity, technology and regulatory professionals to promote responsible AI adoption, strengthen digital resilience and safeguard public trust across Africa.
NAIVASHA, Kenya — Governance, risk management, cybersecurity and technology experts have called for stronger human oversight and accountability in the adoption of artificial intelligence (AI), warning that the rapid advancement of autonomous systems is creating new challenges for institutions seeking to protect sensitive information, maintain public trust and strengthen digital security.
The experts, speaking at the ISACA Kenya Chapter’s GRC 360° Africa Conference 2026 in Naivasha, said organisations must strengthen governance frameworks, improve cybersecurity preparedness and establish clear accountability mechanisms to ensure that AI technologies are deployed responsibly.
They warned that although AI presents significant opportunities to improve efficiency, decision-making and service delivery, its growing ability to perform complex tasks with limited human intervention could expose institutions to new operational, legal and security risks if appropriate safeguards are not put in place.
The conference brought together policymakers, regulators, auditors, board members, cybersecurity specialists, technology practitioners and academics to examine emerging governance, risk and compliance (GRC) challenges in an increasingly automated digital environment.
Discussions focused on how institutions can balance technological innovation with accountability, transparency, regulatory compliance and public confidence as AI systems become more integrated into organisational operations.
Human accountability remains central to AI adoption
Internal Auditor-General at the National Treasury, Dr Sammy Kimunguyi, underscored the importance of accountability, transparency and public confidence in the adoption of artificial intelligence, noting that technological advancement must be accompanied by effective oversight.
He emphasised the need for institutions to ensure that AI systems are introduced within governance structures that clearly define responsibilities, establish safeguards and provide mechanisms for monitoring their performance.
As organisations increasingly explore AI-powered tools to support administrative functions, analyse information and improve service delivery, questions surrounding responsibility for automated decisions are becoming more significant.
The challenge, according to the concerns raised at the conference, is to ensure that the use of AI does not weaken established standards of institutional accountability or create uncertainty over who should be held responsible when automated systems make errors or cause harm.
Human oversight is therefore critical in ensuring that decisions made or supported by AI remain subject to appropriate review, particularly where they affect public services, sensitive data, financial resources or national security.
Institutions must also be able to explain how AI-assisted decisions are reached, identify the individuals responsible for supervising the systems and establish procedures for correcting mistakes.
These measures would help organisations maintain public confidence while reducing the risk of opaque decision-making and uncontrolled reliance on automated technologies.
The emphasis on accountability comes at a time when AI tools are becoming increasingly accessible to businesses, government agencies and other institutions seeking to modernise their operations.
However, experts caution that the ability to deploy new technologies quickly should not be mistaken for readiness to manage the risks associated with them.
AI is making cyberattacks more sophisticated
Cybersecurity emerged as another major concern during the conference, with Dr Kimunguyi warning that advances in AI are making cyberattacks more sophisticated and difficult to identify.
He pointed to technologies capable of imitating human voices and generating convincing fake videos, which can be exploited to deceive individuals, impersonate trusted authorities and facilitate fraudulent activities.
Such capabilities are increasing the potential for social engineering attacks, in which criminals manipulate victims into disclosing confidential information, transferring money or granting access to protected systems.
For instance, a convincing imitation of a senior official's voice could be used to persuade an employee to approve an unauthorised transaction or disclose sensitive information. Similarly, manipulated video content could be circulated to impersonate public figures or spread misleading information.
These threats create additional challenges for organisations that traditionally rely on familiar voices, visual identification or established communication channels to verify the authenticity of instructions.
As AI-generated content becomes more convincing, institutions may need to strengthen verification procedures, introduce additional authentication measures and train employees to recognise emerging forms of digital deception.
Dr Kimunguyi stressed that cybersecurity should be treated as a national security priority, calling for stronger protection of critical information infrastructure, effective incident response mechanisms and compliance with data protection and cybercrime laws.
Critical information infrastructure supports essential services and operations, including government systems, financial services, communications and other digital platforms upon which institutions and the public depend.
A successful attack against such systems could disrupt service delivery, compromise sensitive information and undermine confidence in public and private institutions.
Protecting these systems requires more than deploying technological solutions. It also involves identifying vulnerabilities, monitoring threats, maintaining secure systems and ensuring that organisations can respond quickly when security incidents occur.
Effective incident response is particularly important because even institutions with strong preventive measures may experience security breaches. Having clear procedures for detecting, reporting, containing and investigating attacks can reduce their impact and help organisations recover more effectively.
Compliance with applicable data protection and cybercrime laws is equally important in ensuring that personal information is handled responsibly and that cyber-related offences are addressed through appropriate legal and institutional mechanisms.
Autonomous AI presents new governance challenges
ISACA Kenya Chapter President Bonface Asiligwa called for a shift in traditional governance approaches to address the growing capabilities of autonomous AI systems.
Unlike conventional digital tools that generally perform specific functions in response to direct human instructions, more advanced AI systems can access data, invoke application programming interfaces (APIs) and execute complex sequences of tasks with limited human intervention.
These capabilities can help organisations automate processes, improve productivity and reduce the time required to complete routine activities.
However, they also introduce new risks when systems are granted access to sensitive information, internal applications or operational platforms without sufficient controls.
An autonomous system operating with excessive permissions, for example, could potentially access information beyond its intended purpose, initiate unauthorised actions or propagate errors across connected applications.
Where several systems are linked, a single failure or compromised AI agent could have consequences extending beyond the original point of entry.
Asiligwa's call for a change in governance approaches highlights the need for organisations to reconsider how they assign authority to AI systems and monitor their activities.
Traditional governance models often assume that important decisions and actions are carried out directly by identifiable human employees. Autonomous AI challenges that assumption by introducing systems capable of initiating and completing tasks independently within the permissions they have been granted.
Organisations must consequently establish clear rules governing what AI systems can access, which actions they can perform and when human approval is required.
Such safeguards could include limiting system permissions to essential functions, maintaining records of automated actions, monitoring unusual behaviour and requiring human authorisation for high-impact decisions.
Regular testing and independent assessments may also help institutions determine whether AI systems are operating within approved boundaries and whether their controls remain effective as the technology evolves.
The objective is not necessarily to prevent automation but to ensure that it operates within defined limits and remains subject to meaningful institutional oversight.
Governance gaps pose a systemic risk
Asiligwa also cautioned that one of the greatest systemic risks may not lie in AI itself, but in the widening gap between the speed of technological adoption and the slower development of governance frameworks, organisational capabilities and regulation.
The concern reflects a broader challenge facing institutions that are under pressure to adopt emerging technologies while simultaneously managing security, compliance and operational responsibilities.
When organisations introduce AI tools before establishing appropriate policies, staff training and monitoring systems, they risk creating weaknesses that may remain undetected until an incident occurs.
For example, employees may begin using AI applications to process confidential documents without fully understanding the associated privacy implications. Similarly, departments may adopt different AI platforms without coordinating security standards or clarifying who is responsible for overseeing their use.
Such fragmented adoption can make it difficult for senior management, internal auditors and risk professionals to establish a comprehensive picture of how AI is being used across an organisation.
It may also complicate efforts to assess whether automated processes comply with internal policies and relevant legal requirements.
To address these challenges, governance frameworks must evolve alongside technological capabilities rather than being introduced only after problems emerge.
Boards and executive teams have a particularly important role in setting the direction for responsible AI adoption. They need to understand the risks associated with the technologies their organisations deploy and ensure that appropriate resources are allocated to risk management, cybersecurity and compliance.
Internal auditors and risk professionals can support these efforts by assessing controls, identifying weaknesses and evaluating whether AI-related risks are adequately incorporated into existing enterprise risk management structures.
Regulators, meanwhile, face the challenge of developing and enforcing rules that protect the public without unnecessarily restricting beneficial innovation.
Achieving this balance requires cooperation between government agencies, technology providers, professional bodies and the organisations deploying AI systems.
Strengthening trust through responsible innovation
The discussions at the GRC 360° Africa Conference 2026 also highlighted the importance of collaboration among professionals responsible for governance, risk management, cybersecurity and technology.
As AI applications become more interconnected, risks can no longer be managed effectively by technology departments working in isolation.
Cybersecurity specialists may identify technical vulnerabilities, but internal auditors must also assess whether the relevant controls are functioning as intended. Legal and compliance teams must consider regulatory obligations, while organisational leaders must determine the acceptable level of risk associated with new technologies.
Coordinated decision-making can help institutions identify weaknesses earlier, avoid duplication of controls and establish consistent standards for AI deployment.
Professional collaboration is also important in building organisational capacity. Employees need practical knowledge of how AI systems operate, the risks they introduce and the procedures they should follow when using them.
Training programmes should therefore extend beyond technical teams to include senior managers, auditors, board members and other employees whose responsibilities may be affected by automated decision-making.
Institutions should also develop clear policies governing the use of AI-generated information, the handling of confidential data and the verification of outputs before they are used to support important decisions.
Maintaining trust will depend not only on preventing cyberattacks but also on demonstrating that AI systems are used transparently, responsibly and in ways that respect applicable legal and ethical requirements.
For public institutions, these considerations are particularly important because confidence in government services depends partly on the ability of agencies to protect citizens' information and explain decisions affecting them.
For private organisations, effective governance can help protect customers, preserve business continuity and reduce exposure to reputational and financial losses arising from technology-related failures.
Africa faces an opportunity to strengthen digital resilience
The conference comes as organisations across Africa continue to explore digital technologies to improve service delivery, enhance productivity and support economic development.
AI has the potential to assist institutions in analysing large volumes of information, automating repetitive work and supporting more timely decisions. However, these benefits must be pursued alongside measures that address cybersecurity, privacy, accountability and institutional preparedness.
For African countries, strengthening governance around AI is also an opportunity to build digital resilience and improve confidence in emerging technologies.
This requires investment in professional skills, cybersecurity infrastructure, institutional policies and effective cooperation between regulators and industry.
It also calls for governance approaches that reflect the realities of different organisations, including differences in technical capacity, available resources and exposure to cyber threats.
Rather than treating AI governance as a one-time compliance exercise, institutions need to view it as an ongoing process involving regular risk assessments, continuous monitoring, policy reviews and adjustments as technologies evolve.
The ability to identify emerging risks and respond promptly will be essential as autonomous systems become more capable and more deeply integrated into organisational operations.
The conference's focus on governance, risk and compliance therefore places human oversight at the centre of the debate over responsible AI adoption.
Its discussions are expected to strengthen professional collaboration and advance practical approaches to the deployment of AI across Africa, with a shared emphasis on innovation, resilience, accountability and digital trust.
Ultimately, the challenge facing institutions is to harness the opportunities offered by artificial intelligence without compromising the security, transparency and accountability upon which public confidence depends.
As AI systems acquire greater autonomy, experts are urging organisations to ensure that governance evolves at the same pace as technology, keeping human responsibility, effective cybersecurity and public trust firmly at the centre of Africa's digital transformation.
You Might Also Like
-
EPRA Director General Edward Mwirigi Kinyua has attributed Kenya's latest fuel price increase to rising international petroleum costs, particularly the pressure associated with the conflict in the Middle East. The figures released during the October review show substantial increases in the landed co
-
Ida Odinga's reassurance at Migwena Cultural and Sports Grounds became one of the major talking points during the first anniversary commemoration of Raila Odinga's death on Thursday, October 15, 2026. After sections of the crowd chanted Oburu Oginga's name and demanded to know where he was, Ida exp
-
The university lecturers' demonstrations in Nairobi CBD on Thursday, October 15, 2026, underscored the growing pressure on the government to resolve the public universities' pay dispute. Lecturers marched from the University of Nairobi grounds, demonstrated along Kenyatta Avenue and presented a peti
-
President William Ruto’s development engagements in Baringo have highlighted the government's focus on roads, electricity connectivity, education and security as part of its broader North Rift development agenda. The Sh22 billion road programme targeting 350 kilometres of roads, the electricity c
-
Ida Odinga on Thursday, October 15, 2026, hosted leaders associated with the Linda Mwananchi movement at Opoda Farm in Bondo, Siaya County, ahead of the first anniversary celebrations of the late former Prime Minister Raila Amolo Odinga at Migwena Cultural and Sports Grounds. The delegation included
-
role in elective politics and strengthen her presence in Kenya’s political landscape. Winnie, who currently serves in the East African Legislative Assembly (EALA), has built political experience through regional representation and her involvement in the Orange Democratic Movement (ODM). Her pos